Canopy
Canopy is an AI-native blockchain platform for creating, launching, and developing onchain applications through application-specific networks called Nested Chains. Its infrastructure provides development tools, shared security, governance, interoperability, and a path for Nested Chains to operate as independent networks. [5]
Overview
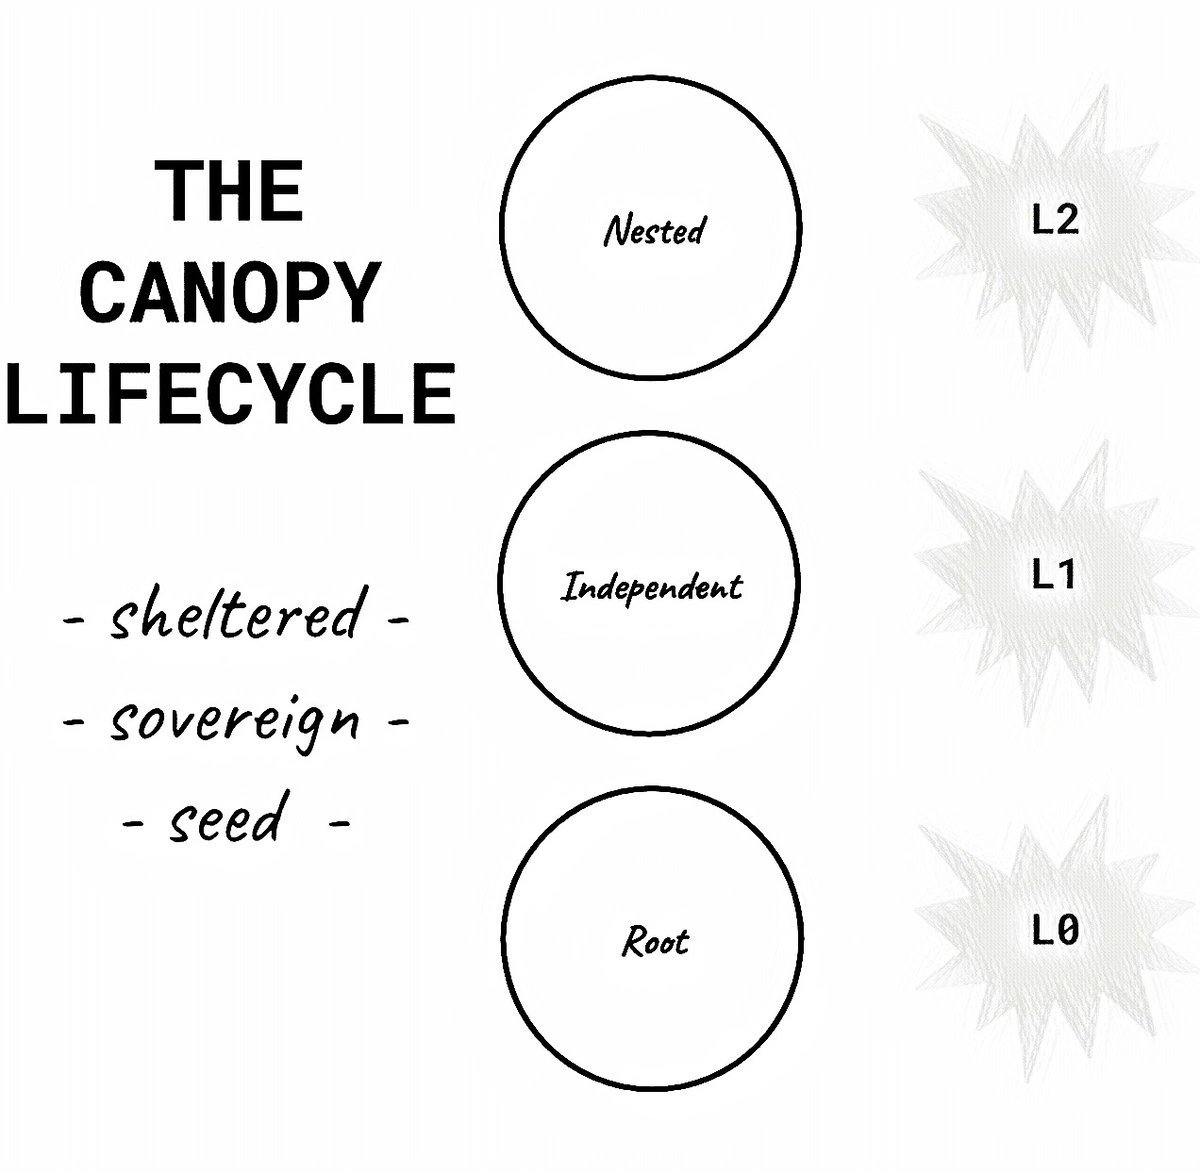
Canopy is an AI-native platform for creating, launching, and developing onchain applications through application-specific networks called Nested Chains. It simplifies development by letting builders start with an idea, use AI to develop and refine application logic, and create prototypes or working applications without first managing consensus mechanisms, validators, or other blockchain infrastructure. The Canopy Stack supports application development using languages including Go, TypeScript, Python, Kotlin, and C#, while the Canopy Terminal provides a process for moving completed applications from development to deployment. Each Nested Chain can have its own application logic, rules, economic model, and governance, giving developers greater control over the environment in which their applications operate.
After launch, Nested Chains can use Canopy Network's shared validator infrastructure and cryptoeconomic security while developing their own user and economic activity. Canopy supports interoperability between Nested Chains without third-party bridges and provides scaling mechanisms that let applications expand across layers or laterally. Its validator ecosystem uses CNPY as collateral, and validators can restake collateral to support multiple Nested Chains. As an application matures, it can continue using Canopy's shared infrastructure or transition toward operating as an independent Layer 1 network, providing a path from an application initially supported by shared infrastructure to a more autonomous blockchain network. [4]
Features
P2P Security
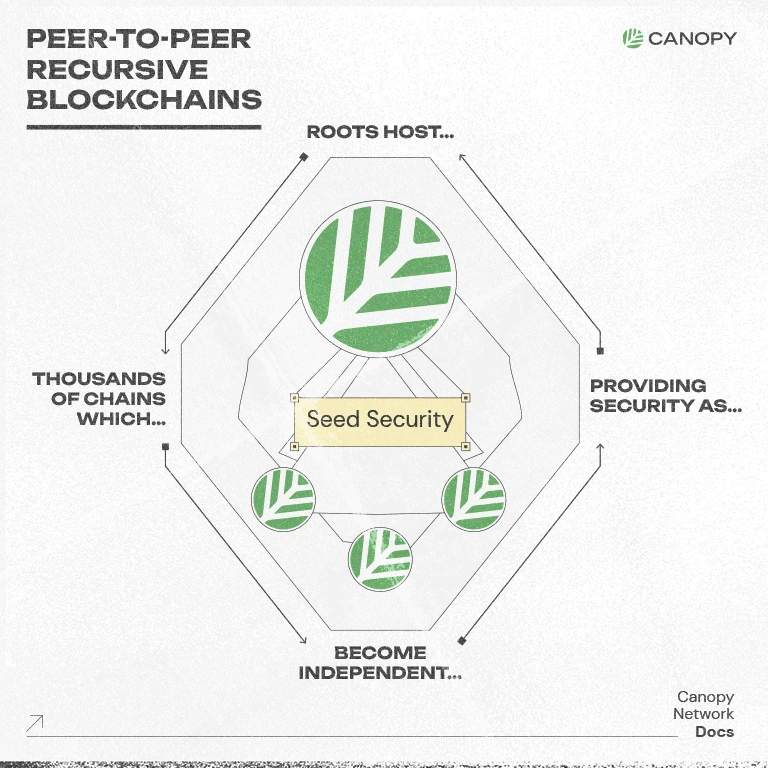
Canopy Network's Peer-to-Peer Security model uses a recursive architecture designed to provide security and infrastructure for newly launched application-specific blockchains while addressing the cold-start challenges associated with independent Layer 1 networks. New chains initially operate under a Security Root chain, which uses its total locked value to help protect against hostile takeovers, provides access to an established validator set, connects the new chain to the broader Canopy ecosystem, and enables liquidity through token swaps with external networks. The model also lets tokens and economic activity circulate between participating chains through mechanisms such as block rewards, connecting the security and liquidity of different networks. As individual chains mature and become sufficiently independent, they can themselves serve as Security Roots for subsequent chains, creating a recursive structure in which established networks provide security and infrastructure for newer ones. The architecture combines an application development model similar to Ethereum's dApp environment with the greater network independence associated with Layer 0 infrastructure, with the security structure expanding as additional blockchains join the network. [6]
Progressive Sovereignty
Progressive Sovereignty is a Canopy framework that lets blockchains gradually operate independently of external protocols and infrastructure. Sovereign blockchains are designed to scale independently, resist censorship by parties outside their stakeholder base, retain complete blockchain history and data ownership, and maintain historical finality when joining or leaving a Security Root. They can also leave or rejoin a Security Root without changing the underlying software, allowing networks to transition toward greater independence over time. [7]
Capital Efficient Restaking
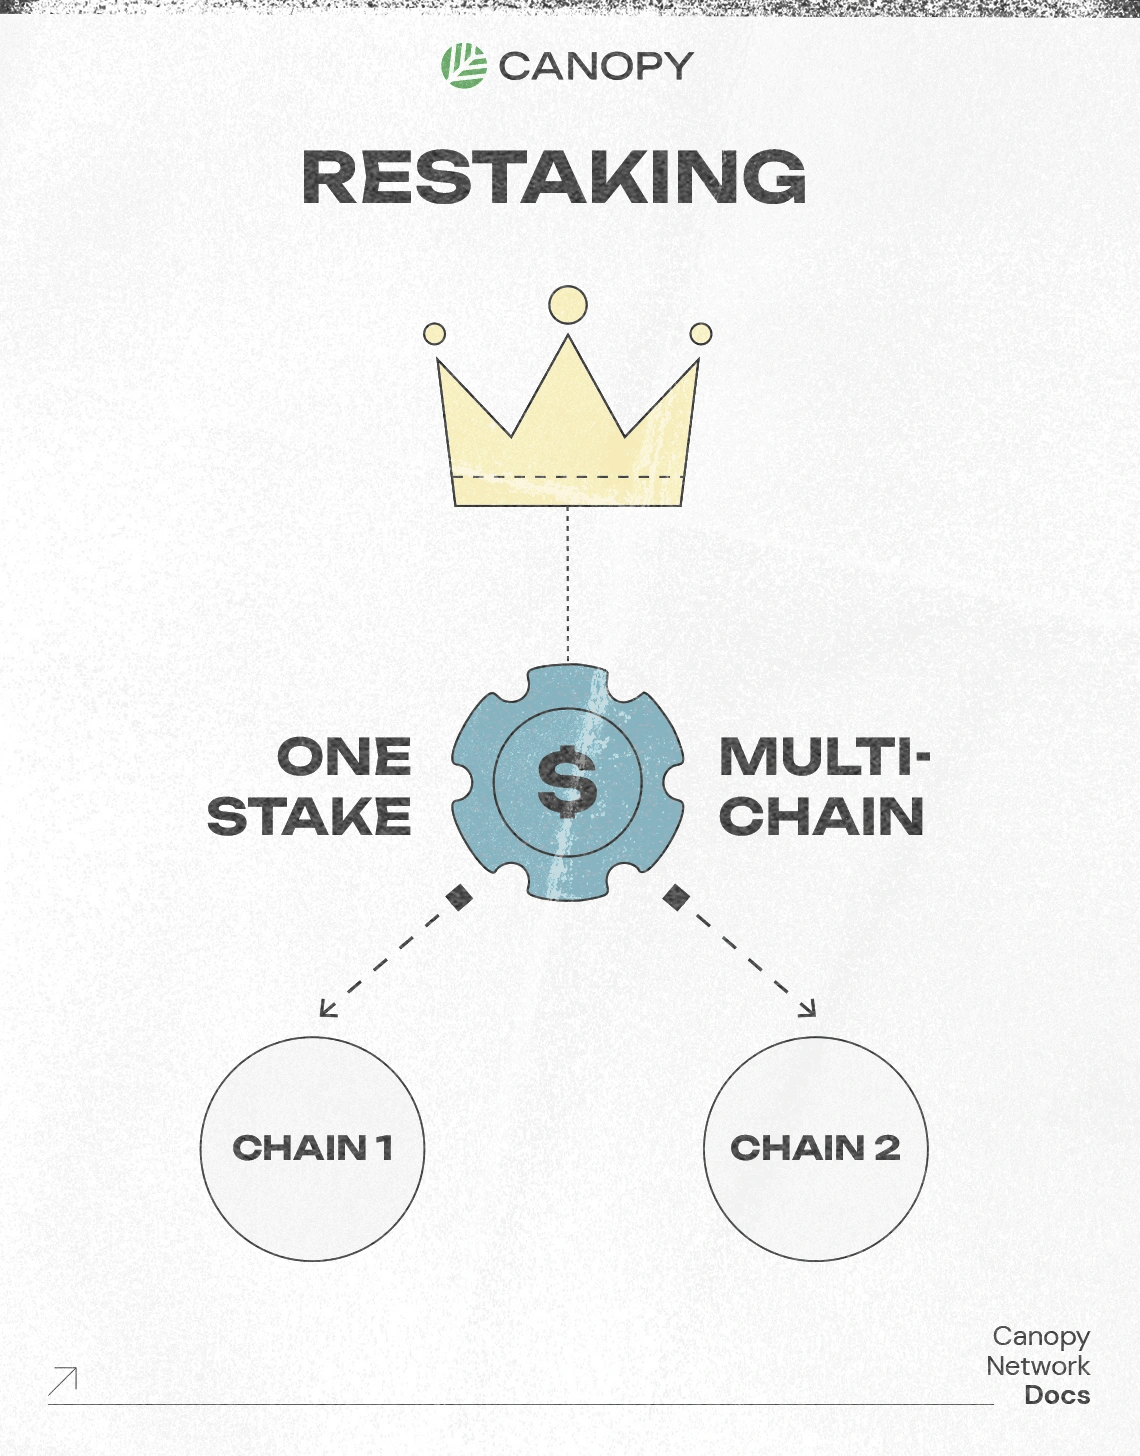
Canopy's Capital-Efficient Restaking model lets validators use existing locked tokens as collateral to secure multiple Nested Chains without providing additional stake for each network. Validators can opt in to support individual chains and receive the respective chain's native token as compensation, while additional rewards may be available through the Security Root based on the amount of committed stake. The Security Root DAO determines how many Nested Chains a validator can support. This model lets new chains obtain security through validator participation and community support, rather than requiring them to independently attract substantial capital for initial security. [8]
Chain Halt Rescue
Canopy's Chain Halt Rescue mechanism helps Nested Chains recover from prolonged periods of non-liveness, where a consensus failure prevents new blocks from being produced. These halts can result from validator outages, protocol non-determinism, or software bugs and may require identifying the underlying issue, updating and distributing blockchain software to a sufficient portion of the validator set, and coordinating validators to restart the network. Canopy's nested architecture allows the Security Root to automatically recover a Nested Chain from a halt, reducing the need for extended manual coordination among validators. This mechanism is intended to shorten recovery periods and maintain continuity of blockchain operations when a Nested Chain experiences a consensus-related disruption. [9]
NestBFT
NestBFT is Canopy's Byzantine Fault Tolerant consensus mechanism for the Root Chain and Nested Chains, designed to provide fast finality, validator fault tolerance, and protection against attacks such as Sybil, DDoS, grinding, and long-range attacks. It combines Proof-of-Stake with Proof-of-Age: PoS provides stake-based consensus, bonding, and economic security, while Proof-of-Age uses Verifiable Delay Functions (VDFs) to establish verifiable elapsed time and help nodes select the correct chain when syncing. The protocol uses a leader-election system based on a practical Verifiable Random Function, with validator stake influencing the likelihood of becoming a leader, while cryptographic inputs make selection difficult to manipulate. NestBFT also uses BLS multi-signature aggregation and a structured communication process to reduce consensus resource requirements.
The consensus process consists of multiple phases covering leader election, proposal, voting, locking, and block commitment, with more than two-thirds of voting power required to pass voting stages. Validators first determine leader candidates using the VRF mechanism, after which a leader proposes a block and validators validate and vote on it. Subsequent precommit and commit stages establish the block's finality, after which validators propagate the finalized block to their peers. If a phase fails, recovery mechanisms allow validators to exchange their current rounds and move to a higher safe round through the protocol's pacemaker, enabling consensus to continue without requiring the network to restart from the beginning. [10] [11]
Canopy KMS
Canopy KMS is a purpose-built key management system that provides signing infrastructure for Canopy's high-value blockchain keys without functioning as a wallet. It separates transaction requests from the systems that hold and use private keys, authenticating and evaluating every request against predefined policies before execution. Rather than returning signed transactions to callers, Canopy KMS builds, signs, and submits approved transactions itself, using a fail-closed policy system that can reject requests that do not meet required conditions. The system supports multiple cryptographic schemes, including ed25519 for Canopy-native transactions, secp256k1 for EVM operations, and BLS12-381 for multisignature and threshold-signature functions. Its signing infrastructure supports operations such as treasury management, cross-chain transfers, multisignature signing, chain creation, and liquidity management, with controls tailored to each transaction type.
Canopy KMS also provides key management services for Nested Chains launched on Canopy, allowing chain operators to use shared signing infrastructure instead of building their own systems. Chain creators can manage treasury wallets for individual chains through the KMS, with configurable spending policies. The system can also support managed bridge operations, including contract deployment, relayer and operator identities, and liquidity management, with each operation subject to the same policy-based signing controls. This creates a common signing boundary for Canopy and its Nested Chains while keeping private keys isolated from the applications and services that request transactions. [12]
CNPY
CNPY is the native token of the Canopy network and is used for transaction fees, network security, and validator incentives across the Security Root and its Nested Chains. Users pay transaction fees in CNPY, with fees based on transaction requirements and network conditions, while validators and delegators bond CNPY to participate in consensus and support committees that secure individual Nested Chains. Bonded CNPY serves as collateral for validator participation, with rewards distributed for following the protocol and penalties, including slashing, applied to malicious or invalid behavior. The network can also use existing bonded CNPY to subsidize security for eligible Nested Chains, allowing new chains to access shared validator security without establishing an independent validator set or raising separate security capital. Governance can direct part of token issuance toward the DAO Treasury to fund activities supporting the broader Canopy ecosystem. [1] [3]
Tokenomics
CNPY has a total supply of 560M tokens and has the following distribution: [1] [3]
- CNPY Block Producers: 70%
- CNPY Staker Delegate: 10%
- Nested Chain Validators: 10%
- Nested Chain Staker Delegate: 10%
Governance
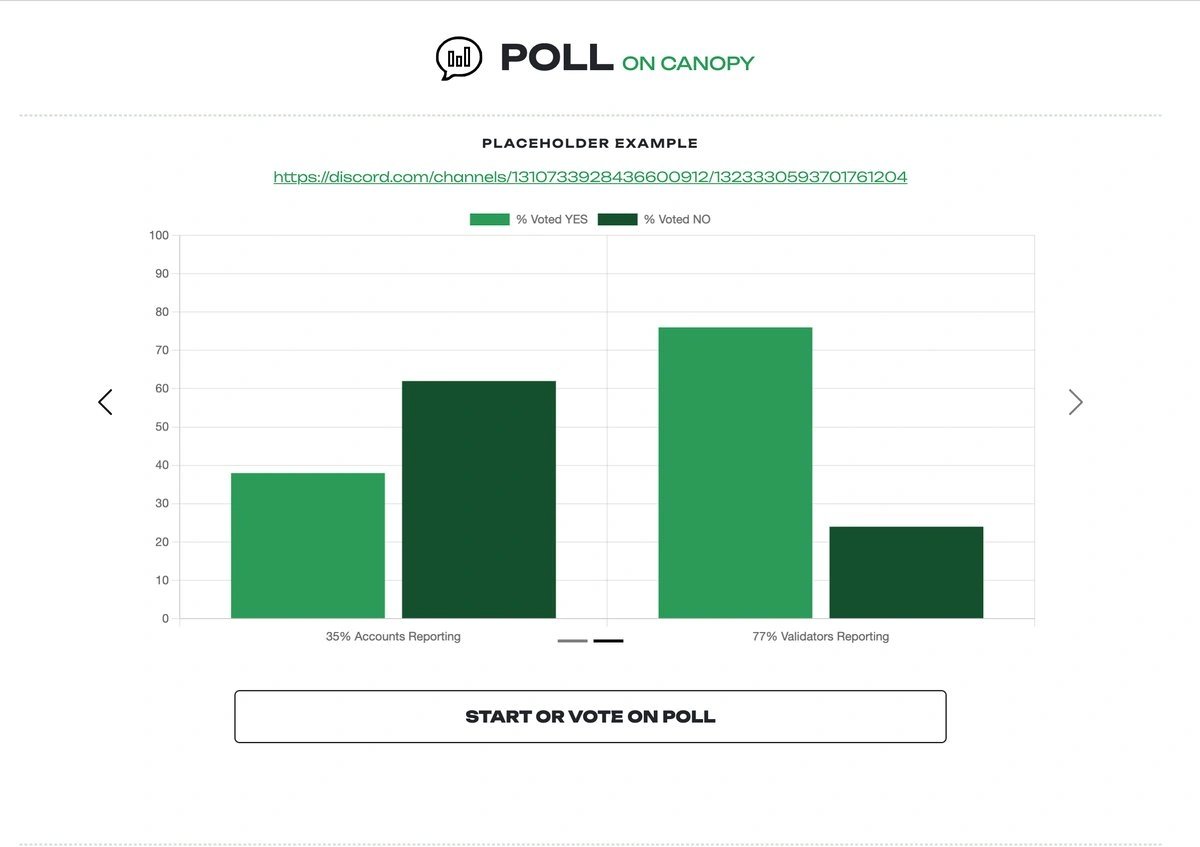
Canopy's United Governance model gives validators a central role in setting each chain's protocol rules, while allowing other ecosystem participants to submit governance polls and proposals. Straw polls enable on-chain voting to measure community sentiment, with voting results separated between accounts holding liquid tokens and validators holding locked tokens. Formal proposals can make certain protocol parameter changes without modifying the underlying code and distribute funds from a chain's DAO treasury. At the broader ecosystem level, Canopy's nested architecture lets individual Nested Chains retain control of their own networks while coordinating through validator representation in Security Roots. Nested Chains can choose to join or leave Security Root systems and can collaborate on shared standards, initiatives, and dispute resolution across the ecosystem. [11]
Partnerships
- Sonic Boom Ventures
- Scytale
- Arrington Capital
- Fenbushi Capital
- SNZ
- KR1
- Borderless
- CodeCraft Group
- Stakely
- Lavender Fire
- Stake Craft
- Rhino Stake
- Kingnodes
- Easy 2 Stake